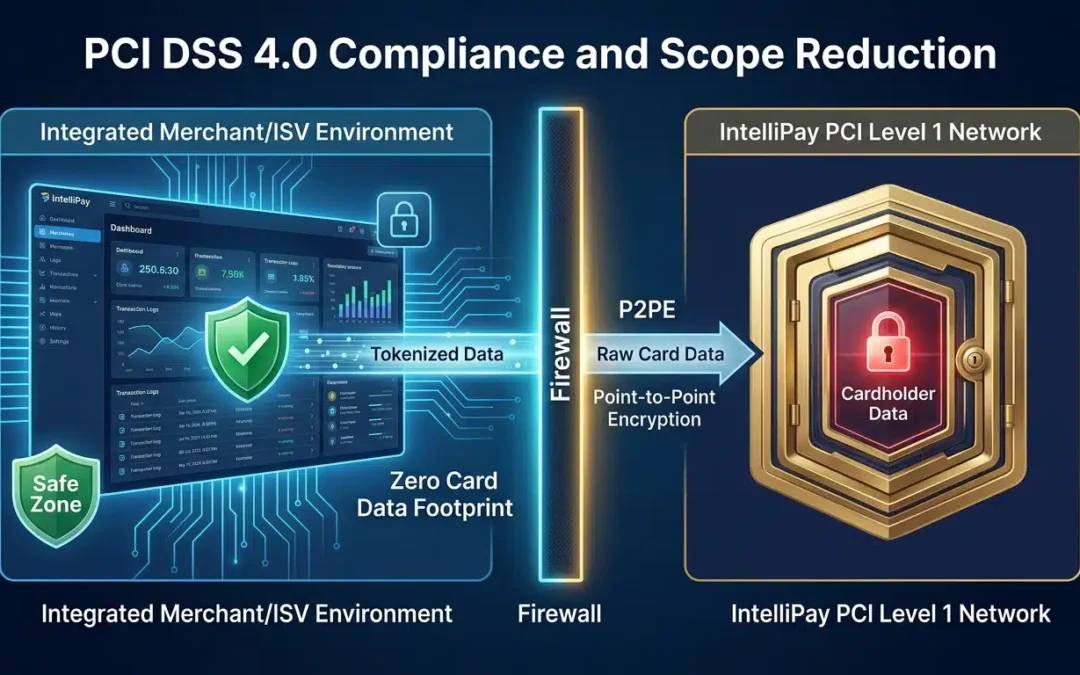

A detailed infographic or technical graphic comparing the audit driven approach of PCI DSS 321 with the outcome based continuous compliance model of PCI DSS 40 web47 The visual highlights key scope reduction strategies such as point to point encryption P2PE and tokenization which move system components out of the cardholder data environment CDE file43 It also emphasizes the new Requirement 1252 for formal scope documentation and the targeted risk analysis TRA approach introduced in the 40 standard web50web53